 Follow Us on Google

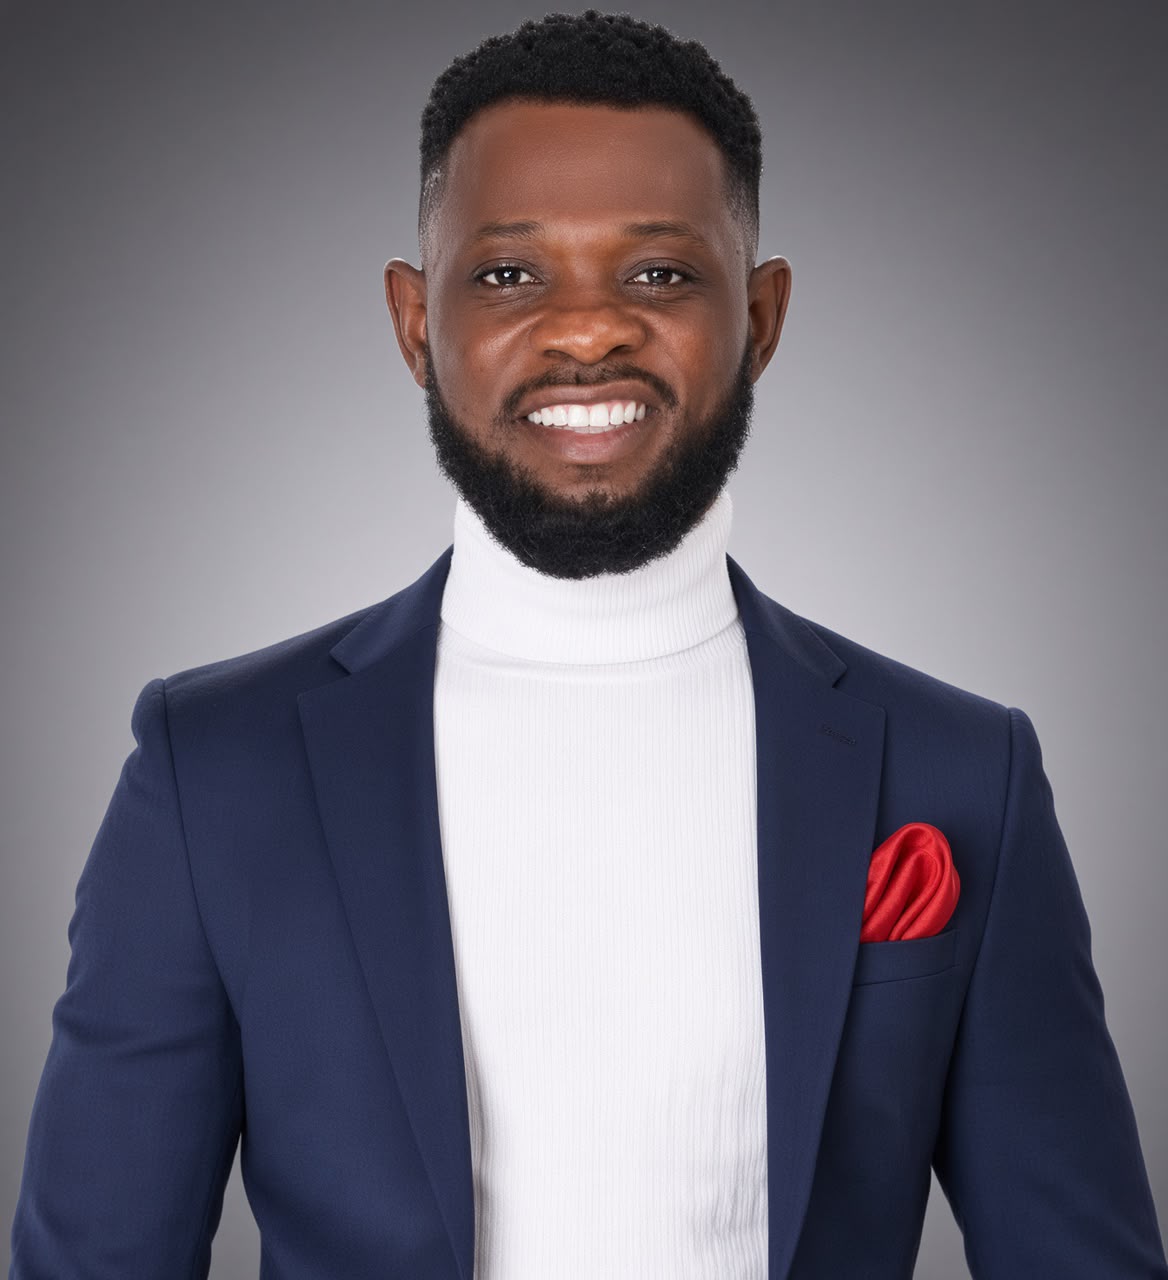
A cybersecurity expert, Olusegun Oludele, has advised digital financial service users to take practical steps to protect their accounts against fraud, unauthorised access and social engineering.
Oludele, Chief Information Security Officer at PalmPay, gave the advice while speaking during the company’s “PalmPay Dey for You” campaign. He said device compromise, poor device security and unauthorised logins were among the factors linked to financial losses recorded in customer complaints and security incidents.
He said users could reduce their exposure to fraud by activating available account-security controls and monitoring unusual transactions.
“Everything comes down to preserving trust,” Oludele said. “We are placing technical control directly into the hands of the end user.”
He highlighted the importance of transaction restrictions during periods when users may be less likely to notice suspicious activity. Such controls allow customers to limit transactions during selected hours and require additional verification before activity can continue.
Oludele also identified social engineering as a major challenge, saying fraudsters often manipulate users into disclosing sensitive information.
“Social engineering is particularly complex because human operators are targeted directly,” he said. “If a user is manipulated into sharing an OTP, PIN or login credentials, technical boundaries can be bypassed.”
He advised users not to disclose their one-time passwords, personal identification numbers or passwords to anyone. He also urged them to avoid suspicious links, unverified customer-service channels and unsolicited requests for account information.
According to him, unusual transactions may be temporarily placed on hold when PalmPay’s security system detects an anomaly. Additional verification may then be required before the transaction is completed.
“Security and user experience must be engineered together,” he said, stressing the need to strengthen protection without unnecessarily disrupting legitimate transactions.
Oludele said effective cybersecurity also required regular internal audits, regulatory assessments, vulnerability assessments, penetration testing and continuous risk reviews.
He described information security as an ongoing process, noting that criminals continually change their methods and attack patterns.
He added that data protection should remain part of security and engineering decisions, with customer information collected and used only for defined purposes such as identity verification, account security and transaction processing.
Oludele advised users to protect their login details, activate relevant security controls and report suspicious activity as soon as possible through verified PalmPay support channels.
“Security works best when the platform and the customer both play an active role,” he said.